Loading certificate in Azure App Service for Linux
In this post, I will explain how you can load a certificate through code in Azure App Service for a Linux container. The steps to use a certificate in Azure App Service are already described in Microsoft documentation. However, I found a couple of gaps in the documentation specifically for Linux. Hence, I decided to write this post.
To follow along you would need an App Service for Linux hosted on Azure.
Why need a certificate
There are various reasons you may need to access a certificate in your code, like encryption/ decryption, authentication, authorization and so on. For example, Raven DB requires a private client certificate to allow access to the data store.
Step 1: Upload your certificate
You can upload the certificate in different ways, such as directly through the portal, Azure CLI or CI/CD pipeline.
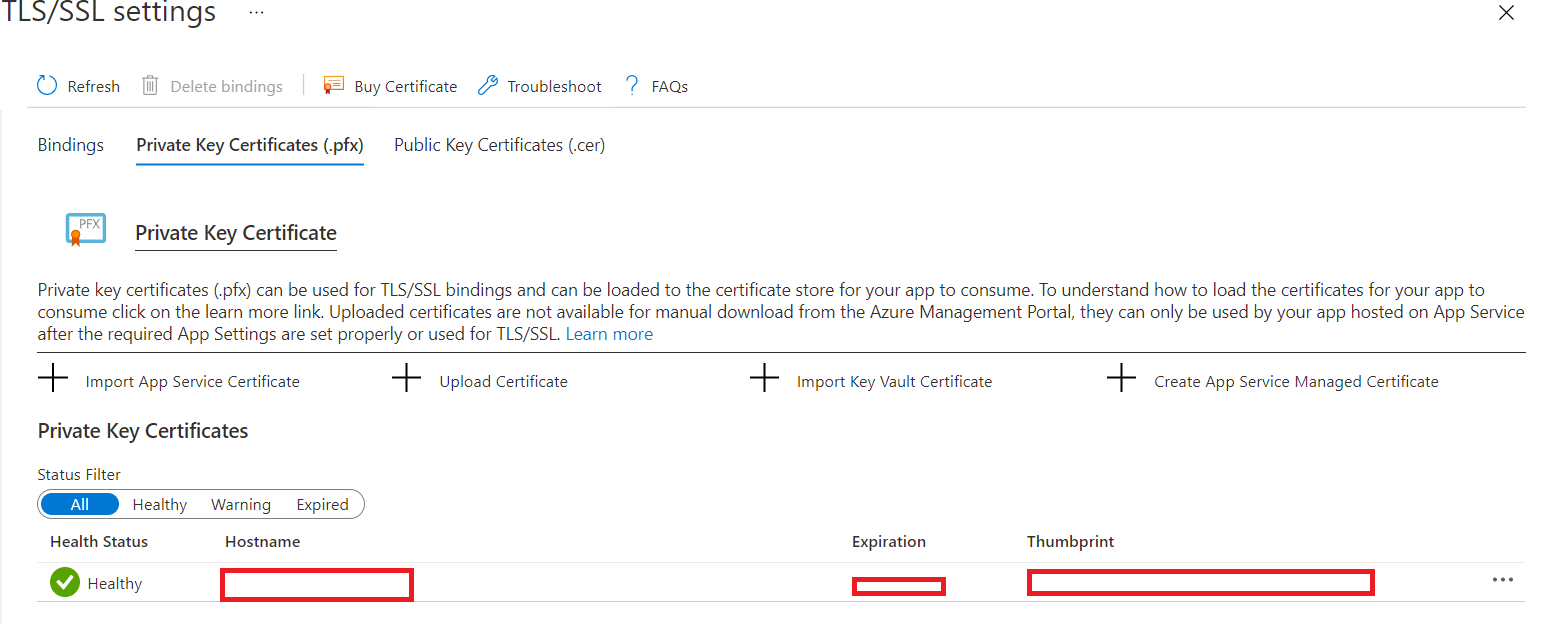
A private certificate uploaded to Azure portal.
Tip: Certificate, its thumbprint and passphrase key for a private certificate are sensitive information. DO NOT store them in your source control.
Step 2: Make your certificate accessible
To access your certificate, through code, you need to make it accessible by creating an app setting WEBSITE_LOAD_CERTIFICATES . WEBSITE_LOAD_CERTIFICATES should be set to comma-separated values of certificate thumbprints.
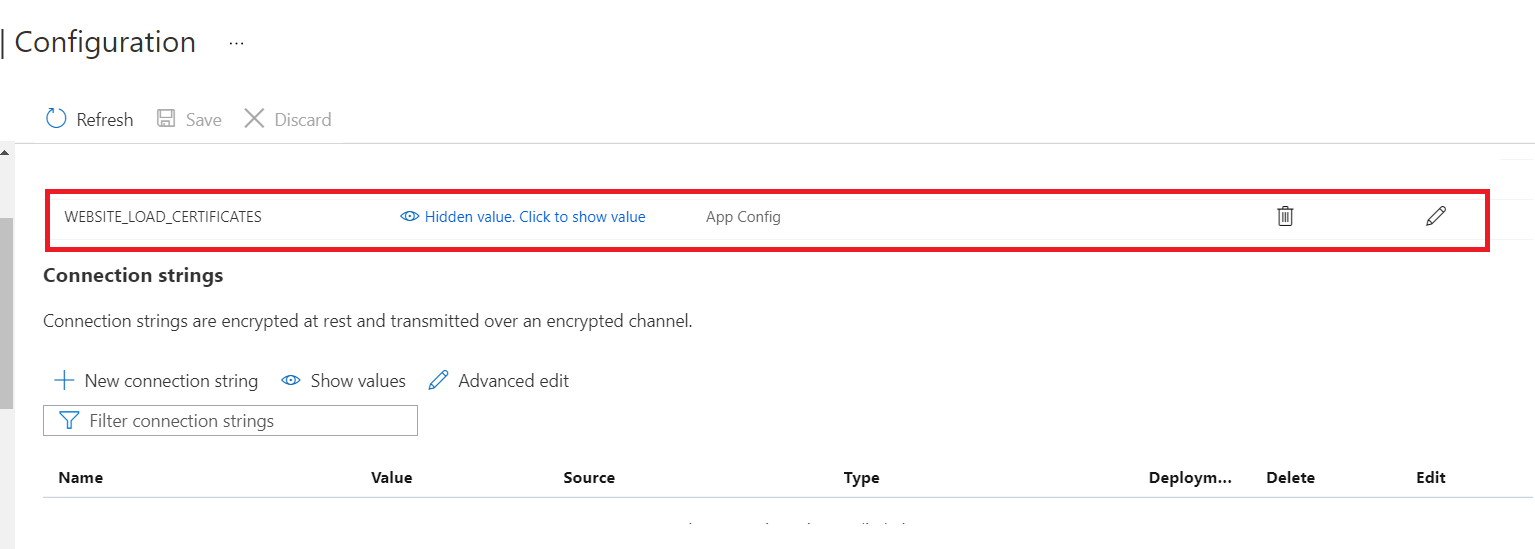
WEB_LOAD_CERTIFICATES app setting
WEBSITE_LOAD_CERTIFICATES is a magic app setting that makes your certificates accessible to your application. For Linux container, it keeps the private certificates at the location /var/ssl/private and public certificates at /var/ssl/certs.
You can view the certificates by logging intossh at https://YOUR_APP_SERVICE_NAME.scm.azurewebsites.net/webssh/host

Note: Azure App service accepts a certificate of .pfx and .cer formats only. It then exposes them as .p12 and .der formats respectively.
For a windows container, Azure App Service automatically exposes the certificate paths through environment variables such as WEBSITE_PRIVATE_CERTS_PATH, WEBSITE_PUBLIC_CERTS_PATH. Unfortunately, you either need to set the environment variables manually or hard code the certificate path in your code for a Linux container.
STEP 3: Accessing certificate in C# code
Finally, you can access certificate in your C# code as shown below:
using System;
using System.IO;
using System.Security.Cryptography.X509Certificates;

public static class CertificateExtensions
{
    // Private certificatePath: $"/var/ssl/private/{thumbprint}.p12"
    // Public certificatePath: $"/var/ssl/certs/{thumbprint}.der"

    public static X509Certificate2 LoadCertificate(string thumbprint, string certificatePath)
    {
        if (string.IsNullOrWhiteSpace(thumbprint))
        {
            throw new ArgumentNullException(nameof(thumbprint));
        }

        if (string.IsNullOrWhiteSpace(certificatePath))
        {
            throw new ArgumentNullException(nameof(certificatePath));
        }

        var bytes = File.ReadAllBytes(certificatePath);
        var certificate = new X509Certificate2(bytes);
        return certificate;
    }
}
Note: To load a private certificate (p12), you do not need to supply a passphrase/ password. I found it the hard way since the code snippet to load a private certificate was missing in the Microsoft documentation. I have raised a PR to fix this. At the time of writing the PR is still in review.
2 comments
Comments were carried over from the previous site and are closed.
Martin Andersson ·
In your Note, it says “you do not need to supply a passphrase/ password.”
We also found out the hard way (after two days of debugging/logging, et.c.) that in fact you SHOULD NOT provide a password, because that was what broke it. Really non-intuitive there.
Thank you anyway for your helpful post.
tutike2000 ·
Sadly I’m just getting an “You do not have permission to view this directory” exception when trying to read the certificate. I can see the file when SSH-ing into the server